01
Multi-Tenant Architecture
We design pooled, siloed and hybrid tenancy models around your cost and compliance needs. Each gets clear isolation rules.
SaaS platforms run continuously across tenants, regions, and release cycles. Our teams start where delivery usually breaks first.
Manual deployments make every release a late-night event. We automate release management to avoid last-minute fixes.
One outage on a shared platform hits every tenant. We set reliability targets early to prevent incidents.
One heavy tenant should never slow down another. We design isolation that protects performance, data, and contracts.
Idle resources and oversized clusters quietly drain margins. Our cloud cost optimization gives every team ownership of their spending.
Buyers ask for SOC 2 compliance evidence before signing. We build SaaS security controls that keep deals moving.
Product engineers lose days to environments, pipelines and incidents. Our platform engineering returns that time to features.
Our DevOps consulting services cover how SaaS products are built, released and run. We work inside your cloud, tools and team.
We use DevOps automation to build CI/CD pipelines with tests, quality gates and rollbacks. Teams ship small changes often and calmly.
Our Kubernetes consulting team designs, migrates and runs clusters that scale with tenant demand. Autoscaling and GitOps come built in.
We use Terraform and Ansible to make environments repeatable and reviewable. New regions launch from code, not tickets.
Our site reliability engineering practice defines SLOs, error budgets and on-call runbooks. We fix issues before customers notice.
Our DevSecOps consulting embeds scanning, secrets management and policy checks into every pipeline stage. Risks surface during development.
Our cloud and DevOps engineers apply FinOps practices so teams see what services cost. We rightsize workloads without hurting performance.
We review your pipelines, infrastructure, security and cloud spend in one session. You leave with a prioritized action plan, free of obligation.
A SaaS platform must serve many customers safely on shared infrastructure. We design these patterns for production, then run them long term.
We design pooled, siloed and hybrid tenancy models around your cost and compliance needs. Each gets clear isolation rules.
Network policies, per-tenant encryption and access controls keep customer data separate. Audit trails make it review-ready.
We structure services, gateways and queues so teams deploy independently. Clean APIs make SaaS integration predictable.
Blue-green and canary releases shift traffic gradually and roll back automatically. Customers keep working while you ship.
We build failover and recovery plans around agreed RTO and RPO targets. Regular drills prove they work.
Autoscaling and queue-based processing absorb traffic peaks and seasonal demand. Spend follows revenue at scale.
SaaS security works best when controls live inside the delivery pipeline. Audit evidence then builds up naturally from daily work.
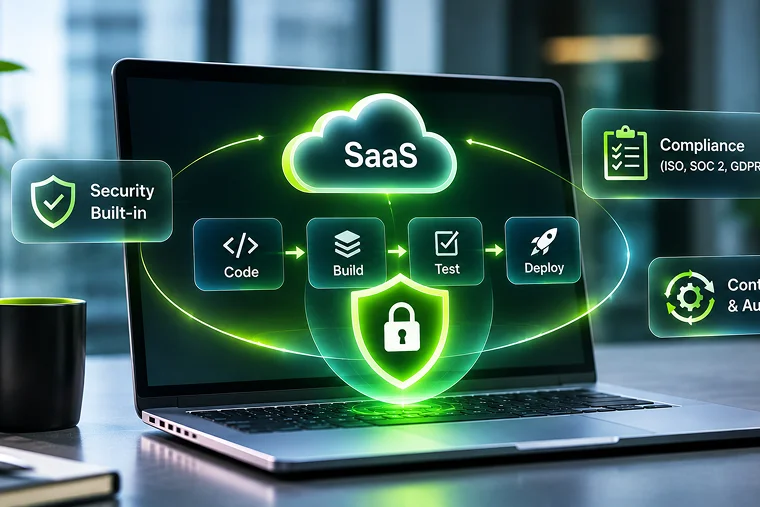
We map pipelines and infrastructure to SOC 2 trust criteria and close gaps. Auditors receive system evidence, not screenshots.
We implement technical controls that support ISO 27001 and GDPR. Your team keeps ownership of policy and certification.
We set up vault-based secrets, least-privilege roles and short-lived credentials. Every access change stays logged.
We run code, dependency, container and infrastructure scans on every build. Critical findings stop the release.
We use Open Policy Agent guardrails to enforce configuration rules everywhere. Each change leaves a permanent record.
We document architecture and controls so vendor security reviews move faster. Sales teams stop waiting on engineering.
We embed AIOps into SaaS operations so noisy telemetry becomes early warnings. For AI products, we also cover model delivery and GPU cost.
Our machine learning models group related alerts and flag anomalies early. On-call engineers see one incident, not fifty alerts.
We connect metrics, logs and traces to show how each tenant behaves. Teams reach root causes without guesswork.
We use usage patterns to drive scaling decisions before demand peaks. Performance stays steady and spend proportionate.
We automate training, evaluation, deployment and monitoring for models and LLM features. Versioned releases keep AI auditable.
We use scheduling, spot capacity and utilization tracking to control GPU spend. AI features stay affordable as usage grows.
We build internal developer platforms with golden paths and self-service environments. Engineers launch services without infrastructure tickets.
Financial SaaS runs on money, identity data and strict regulators. Our delivery and controls hold up under audit and load.
Lending platforms run origination, scoring and collections on tight turnaround times. We keep every workflow available and auditable.
Payment platforms must process transactions without drops or duplicates. We ship zero-downtime releases with PCI DSS aligned controls.
Trading apps face sharp load spikes at market open. We use autoscaling and low-latency observability to keep dashboards fast.
Compliance products handle sensitive identity data under strict retention rules. We enforce encryption, access logging and policy as code.
Mobile-first banking products release often and cannot tolerate outages. We use multi-region setups and canary releases.
Claims platforms connect to many partner systems. We keep those links dependable with stable APIs and tested rollbacks.
Every industry brings its own uptime, compliance and cost pressures. We tailor delivery, security and scaling to the platform, not to a template.
Lending, payments, wealth, KYC and digital banking platforms need zero-downtime releases and audit-ready controls. We pair PCI DSS aligned pipelines with low-latency observability.
EHR, telemedicine and hospital management platforms run on multi-tenant architecture and sensitive patient data. We design isolation, encryption and audit logging that support HIPAA safeguards.
Order management, subscription billing and storefront platforms face sudden traffic peaks and strict billing cycles. We use autoscaling, load testing and automated pipelines to keep checkout fast.
Fleet tracking, warehouse and supply chain platforms ingest real-time data through many integrations. We use auto-scaling, monitoring and stable APIs to keep SaaS integration dependable.
Learning platforms, virtual classrooms and assessment tools face heavy load during admission and exam peaks. We scale capacity on demand and keep student data separated across tenants.
HRMS, payroll, CRM and collaboration platforms serve many enterprise tenants with strict uptime needs. We deliver tenant isolation and release discipline that satisfy enterprise security reviews.
Our DevOps consulting services apply proven DevOps best practices and end each step with defined outputs. You see progress and risks at every step.
We review architecture, pipelines, security posture and cloud spend. You receive a ranked list of risks and quick wins.
We agree on targets for release frequency, reliability and cost. A phased plan sequences work around your product calendar.
We create landing zones, infrastructure as code and base pipelines first. These foundations make every later step safer.
Our DevOps automation moves services onto CI/CD and containers in phased waves. Release management and tested rollbacks protect every wave.
We add monitoring, alerting, security controls and runbooks, then train your engineers. You own the platform, with no lock-in.
After launch, our managed DevOps services track performance and fix issues where necessary. Or we support your in-house team.
From slower releases to stronger security, our case studies show DevOps in daily operations. Each startup faced growth pressures SaaS teams will recognize.
Challenge: A growing FinTech startup needed infrastructure to expand digital wallet, payment and investment services without compromising security or reliability.
The Solution: We built a security-first, automation-driven platform with DevSecOps, Snyk and Aqua Security scanning, and Docker containerization.
Results:
Challenge: Manual deployments, infrastructure management issues and longer delivery cycles could not keep pace with growing application demand.
The Solution: We deployed AWS infrastructure with Kubernetes orchestration, automated CI/CD pipelines, automated testing and infrastructure automation.
Results:
Challenge: A platform combining movie tickets, music, video and merchandise had to stay consistent while traffic and operational demands grew.
The Solution: We redesigned delivery around automation using Terraform, Ansible, Jenkins and GitLab CI/CD pipelines with automated testing.
Results:
As a DevOps services company, we pair proven DevOps best practices with clear communication. Our engineers act as part of your team.
We have delivered 500+ projects across 50+ technologies. That experience shortens the learning curve.
More than 100 DevOps experts work together under one roof. You avoid coordinating separate vendors.
Choose fixed-scope projects, managed services or dedicated DevOps engineers. Change models as your team grows.
Security is part of every design review, not an afterthought. Customer audits stay predictable.
Our Gurgaon-based engineers bring senior expertise at competitive rates. Flexible hours align with US, UK and EU time zones.
Our clients report a 95% satisfaction rating across engagements. We measure success by your release speed and uptime.
Talk to a DevOps engineer about your pipelines, infrastructure and compliance goals. Share your challenge and we will propose a clear next step.
Talk to a DevOps Expert