01
Microservices & Cloud-Native Applications
Create independent pipelines for each service, with shared templates, container builds, and GitOps-based deployment across clusters, environments, and cloud regions.
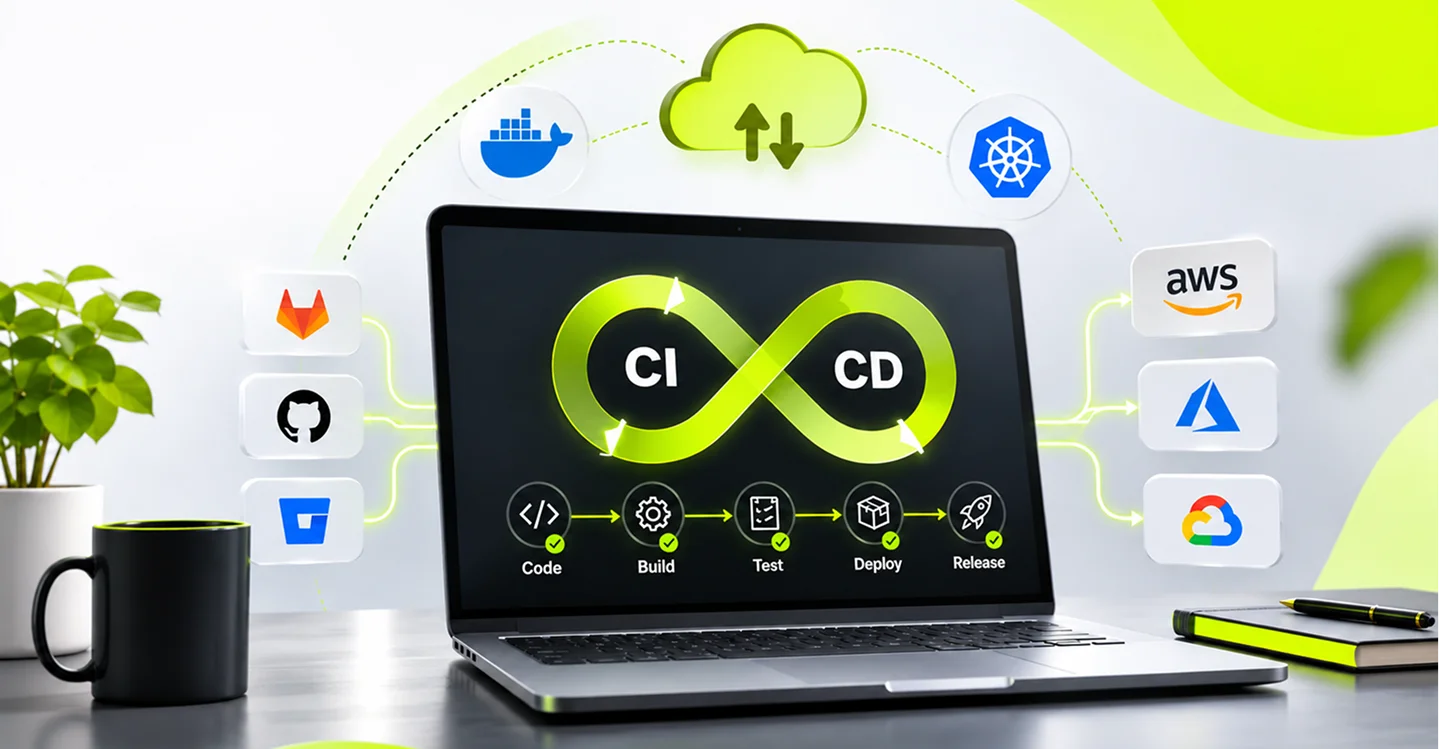
Our CI/CD pipeline services design, build, secure, and run the continuous integration and continuous delivery automation that takes your code from commit to production. From GitHub Actions and GitLab CI/CD to GitOps-based delivery on Kubernetes, our DevOps CI/CD pipeline solutions commit a time frame of 24 hours to 40 hours. This helps your teams release more often, catch defects earlier, and stop relying on manual handoffs.
Writing code is only part of delivering software. Builds run slowly, tests fail for unclear reasons, security checks arrive at the end, and releases still depend on a few people who know the manual steps. Every delay slows the product team and makes each change riskier.
Our CI CD consulting services give your engineers one automated path from commit to production. We assess how code moves through your organization today, then design and implement CI/CD pipeline solutions with automated testing, built-in security, GitOps-based deployment, and clear delivery metrics, so releases become faster, safer, and easier to repeat.
Our CI/CD pipeline services cover the full path from the first commit to a monitored production release. We design, automate, secure, and continuously improve each stage, with clear ownership and measurable delivery metrics.
We design pipelines around how your teams already build and ship, so code moves from commit to release through one consistent, automated path.
Every commit is built and verified automatically, so defects surface within minutes, and the main branch stays ready to release.
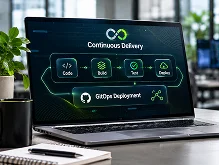
We automate releases to every environment with Git as the single source of truth. Backed by our Kubernetes consulting services, your pipelines deploy clusters across cloud and hybrid environments.
CI/CD pipeline security checks run inside every build as standard steps, so vulnerabilities are found early, and every build artifact can be traced and verified.
We provision and update cloud environments through version-controlled code, so development, staging, and production stay consistent and easy to recreate.
We measure how your pipelines perform, remove slow and unreliable stages, and keep them running smoothly as your tools, teams, and workloads change.
Get a CI/CD pipeline designed around your stack, security requirements, and release cadence.
CI/CD is not only about automation. Its broader value comes from making every release smaller, safer, and easier to repeat, so teams can ship improvements without disruption.
Automated build, test, and deployment steps replace manual handoffs and shorten the time from commit to production.
Automated testing and quality gates catch defects before deployment, reducing rollbacks and emergency fixes.
Developers get build and test results in minutes, so they spend less time waiting and more time building.
Scanning, secrets detection, and policy checks run automatically on every commit, not only before major releases.
Infrastructure as Code and containerized builds keep development, staging, and production aligned and reproducible.
DORA metrics and pipeline dashboards show exactly where delivery slows down. Our DevOps automation services can extend this across the wider delivery lifecycle.
The right DevOps CI/CD pipeline tools depend on your source control, cloud platform, application architecture, and security needs. At DevOps Experts India, we build on the CI/CD pipeline tools you already use and recommend changes only where they add clear value.
 GitHub Actions
 Jenkins
 GitLab CI/CD
 CircleCI
 Azure Pipelines
 AWS CodePipeline
 Bitbucket Pipelines
 Helm
 Terraform
 PulumiAWS CDK
 Azure Bicep
 Docker
 KubernetesAmazon EKSAzure AKS
 Google GKE
 Red Hat OpenShift
 SonarQube
 Snyk
 Trivy
 Prometheus
 Grafana
 Datadog
CI/CD pipeline solutions should fit how your teams already work, not force a full tool replacement on day one. Our approach is staged, transparent, and tied to measurable delivery results.
Review repositories, branching, build and test stages, release steps, environments, security checks, and delivery metrics to find where time and quality are lost.
Agree on tooling, environments, deployment strategy, security gates, and success measures, so the design reflects your goals, team structure, and compliance needs.
Implement CI pipelines, automated tests, artifact management, and infrastructure as code, using reusable templates that teams can adopt across services.
The approach we follow for our DevSecOps consulting services adds vulnerability scanning, secrets detection, artifact signing, and policy checks, so security runs inside the pipeline instead of after it.
Introduce GitOps-based delivery with progressive rollouts, automated approvals, and rollback, starting with one service and expanding in stages.
Track delivery metrics, tune build time and cost, document pipelines, and train your engineers. Ongoing support is available through our DevOps managed services.
From first assessment to GitOps-based releases, get a clear plan for faster, safer software delivery.
Every application type has its own architecture, release model, and compliance needs. We shape each CI/CD pipeline around the environment it serves.
Create independent pipelines for each service, with shared templates, container builds, and GitOps-based deployment across clusters, environments, and cloud regions.
Coordinate builds, approvals, and releases across multiple teams, dependencies, and environments while keeping deployment standards consistent, auditable, and easy to govern.
Support frequent releases with automated testing, feature flags, and progressive rollouts, so product updates reach customers quickly without disrupting existing users.
Automate iOS and Android builds, code signing, testing, and store distribution, so mobile releases follow the same reliable path as your backend services.
Extend pipelines to data workflows, model packaging, and deployment, using versioned artifacts, validation checks, and reproducible environments for reliable analytics and AI releases.
Add approval gates, audit trails, signed artifacts, and policy-as-code to meet security and compliance requirements without slowing the pace of delivery.
At scale, pipelines need more than automation scripts. They need shared standards, built-in security, and a model that improves delivery performance over time.
Reusable templates and shared workflows give every team an approved starting point for new services, while leaving room to adapt pipelines to the needs of each application.
Scanning, artifact signing, approvals, and audit trails are part of every pipeline run, so governance scales with the number of teams, repositories, and releases across the organisation.
Caching, parallel execution, and right-sized runners keep build and test times low, even as repositories, teams, and test suites continue to grow, protecting developer productivity.
DORA metrics, pipeline traces, and failure analytics show where delivery slows down, so teams can fix root causes with data instead of guesswork and track improvement over time.
Progressive rollouts, automated health checks, and tested rollback paths limit the impact of a faulty change and restore service quickly, without lengthy manual intervention.
Pipeline-as-code, architecture records, and runbooks keep delivery knowledge in the repository rather than with individual engineers, improving continuity as teams, tools, and projects change.
We at DevOps Experts India provide CI/CD consulting services and CI/CD pipeline implementation that make software delivery faster, safer, and easier to scale.
Pipeline scope, tooling, and release strategy are shaped around your product goals, team structure, compliance requirements, and technology environment rather than a fixed template or standard package.
From source control and CI/CD to infrastructure as code, security, observability, and Kubernetes, our engineers can design and improve the complete path from the first commit to a monitored production release.
Our team works across AWS, Azure, Google Cloud, Kubernetes, GitHub Actions, GitLab CI/CD, and Azure DevOps, choosing tools that fit your environment and team instead of pushing a fixed vendor stack.
Every engagement starts with baseline delivery metrics and reports of progress on deployment frequency, lead time, failure rate, and recovery time, so improvements are visible, measurable, and tied to business outcomes.
Documentation, reusable templates, and hands-on handover sessions give your engineers full ownership of every pipeline we build, reducing long-term dependency on individual engineers or external teams.
Start with an assessment, a single-service pilot, or a full implementation, then add ongoing support as your needs grow. You can also hire DevOps engineers to work alongside your team.
Get faster releases, safer deployments, and pipelines your team can own, without slowing product delivery.
Get a free CI/CD Pipeline Assessment!